Security begins with Clarity.
Pentesting. Red Teaming. With Impact.
Pentesting.
Red Teaming.
With Impact.

Over 150 projects for >70 clients.

Human. Independent. Effective.

Various hands-on certifications.
ISO 27001
MindBytes is ISO/IEC 27001 certified
Certified in pentesting
such as OSCP, OSWE, OSEP, BSCP, and CAPE
Certified in red teaming
such as CRTO I & II, CARTP, CRTP, and CRTE
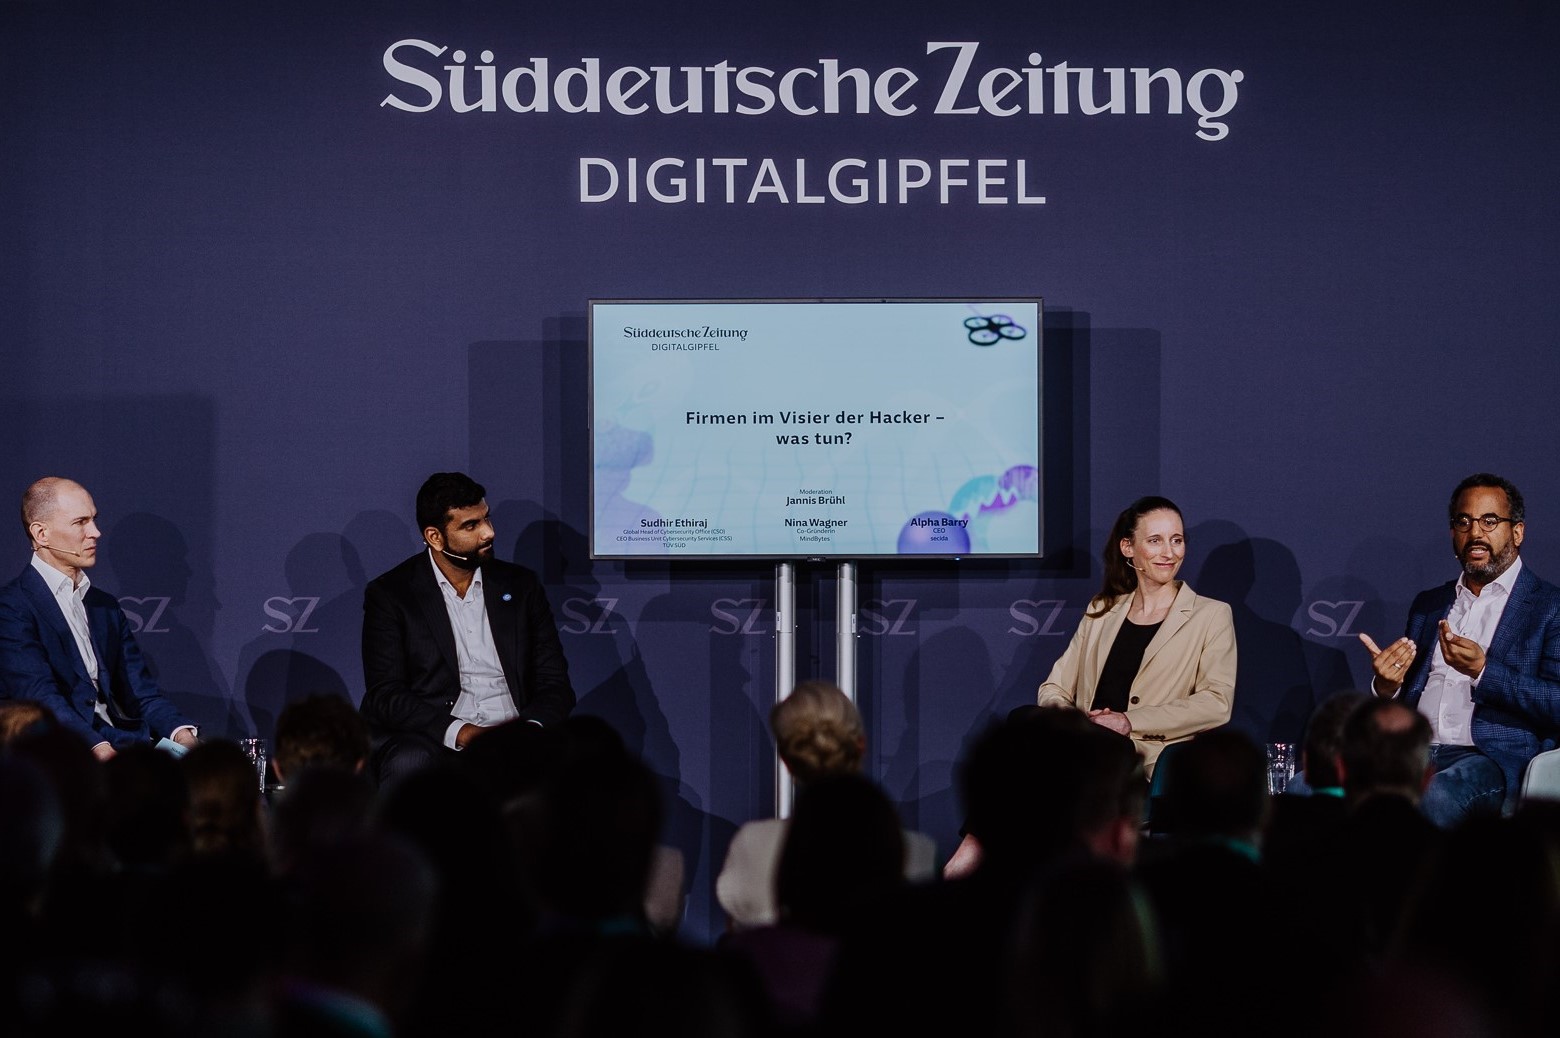
Security community
active with technical contributions, presentations, and CVEs
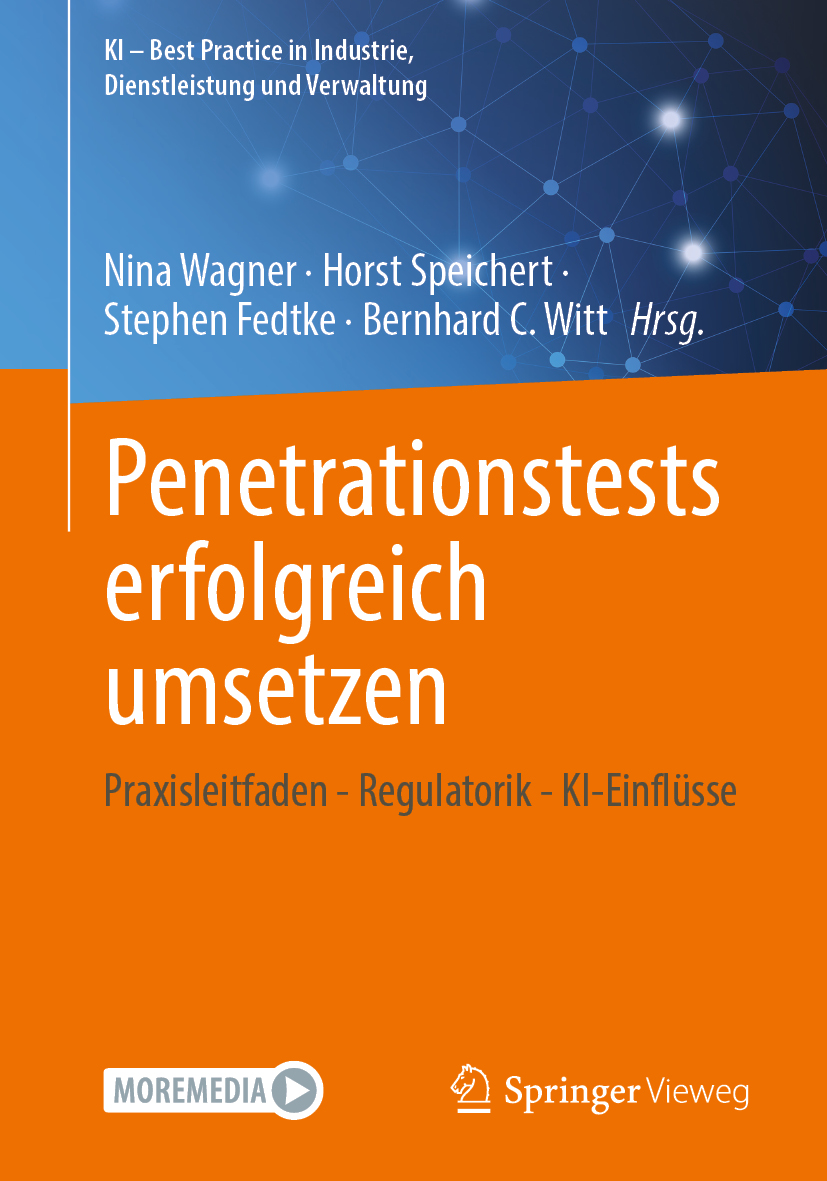
Technical book
Co-editor, published in 2025 by Springer Vieweg
Pentesting. Red Teaming. With Impact.
We work with you to maximize the impact of your project.
Driven by personal collaboration, top-tier quality, and clarity — for everyone from technical teams to management.
Pentesting
Efficiently uncovering vulnerabilities.
In pentests, we uncover vulnerabilities in specific systems, infrastructures, and applications. By providing proof of exploitability, you can immediately see which gaps are actually relevant in practice.
Red Teaming
Simulating realistic attacks.
In red teaming, we conduct realistic attacks on the entire company. We look for attack vectors in IT systems as well as in people, processes, and physical measures—exactly how a real attacker would proceed.
Who We Are
After 3 years together at an IT security company, we – Christian, Nina, and Simon – founded MindBytes GmbH in 2023 to implement our own vision of great projects: personal contacts, fast processes, and practice-relevant qualifications.
Since our second year, we have been continuously hiring more pentesters and have quickly doubled in size. What matters most to us in our employees is that they are committed and passionate about what they do, burn for their topics, and don’t let up until they have extracted the maximum added value for the client from their projects.
What defines us
Personal, efficient, flexible
Through personal contact, we can react quickly and respond to your needs. Lean processes ensure swift execution.
ISO 27001 + Personenzertifikate
Seit 2025 sind wir ISO-27001-zertifiziert. Fachlich beweisen wir uns regelmäßig mit diversen Personenzertifikaten, die zu den anspruchsvollsten der Branche gehören.

Aktiv in der Security-Community
Wir teilen unser Fachwissen auf Events, in Podcasts, auf LinkedIn und in einem Fachbuch über Pentesting, das wir selbst mit herausgegeben haben.

Unsere Berichte
Weil ihr maximalen Nutzen aus eurem Projekt mitnehmen sollt, legen wir größten Wert auf einen übersichtlichen, verständlich aufbereiteten Bericht – mit einer Zusammenfassung für das Management und klaren, priorisierten Handlungsempfehlungen sowie Details für die Techies. Spätestens 5 Werktage nach Testende habt ihr ihn.

Worst-Case-Szenarien
Was ist das Schlimmste, was eurem Unternehmen passieren könnte? Was darf in dieser Anwendung auf keinen Fall schiefgehen? – Das fragen wir euch, um einzuschätzen, worauf wir beim Testen den Fokus legen. Im Bericht erfahrt ihr, ob der Worst Case tatsächlich eintreten könnte – und machen die technischen Ergebnisse damit greifbarer.
Process
5 steps from first contact to project completion:
Get the provider selection checklist
So that your project actually fits your goals.
Receive our 10 Key Questions for Vendor Selection for Pentesting and Red Teaming. To ensure you don’t order a pentest and receive a vulnerability scan.
Click here to request the checklist by email.
Bonus: Do you have an offer and are unsure?
We would be happy to take a 15-minute look at it with you – with no obligation, of course.
Checkliste zur Anbieterauswahl sichern
Checkliste zusenden an:
News
Publications
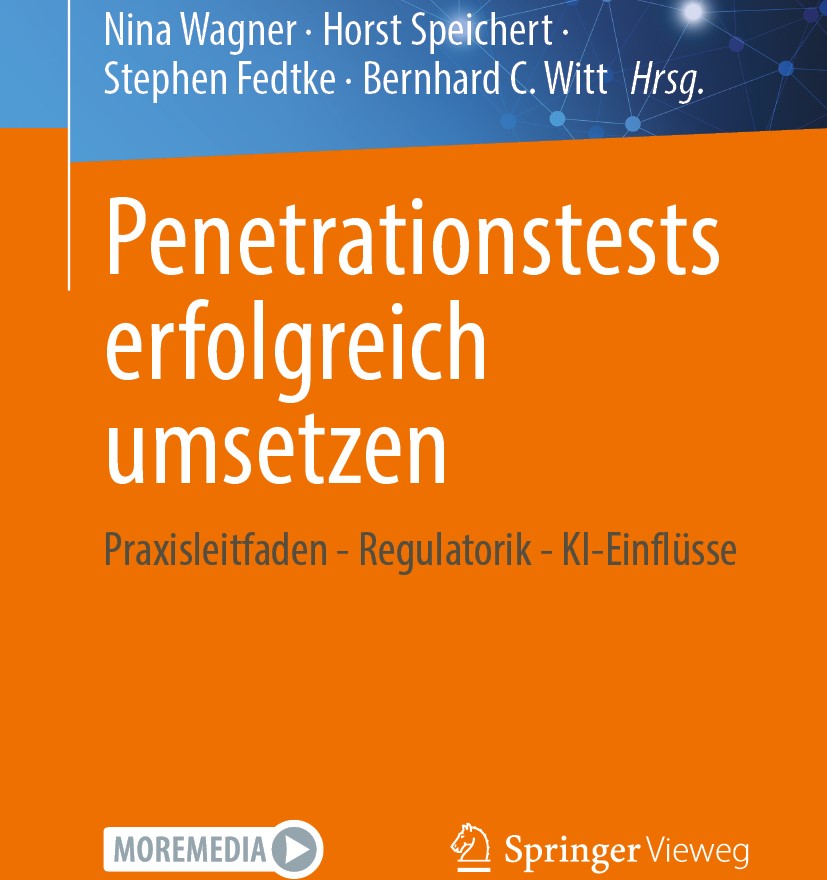
Technical book “Successfully Implementing Penetration Tests”
Springer Vieweg, June 2025.
Available, for example, on Amazon.
CVEs
Details zu veröffentlichten Schwachstellen findet ihr im Blog mit dem Tag “CVE”.
Upcoming events
New on the blog
From London to the Alps: June didn’t stand a chance of being boring.
Team Meeting June: From London to the Alps: June didn’t stand a chance of being boring …
May brings new beginnings – here’s what’s been happening with us (and what’s still to come).
May brings new beginnings – here's what's been happening with us (and what's still...
OWASP Top 10 – Update
We summarize what has changed and what this means for work…
Project in Planning?
Whether it's a pentest, red teaming, or a custom request –
we look forward to speaking with you!