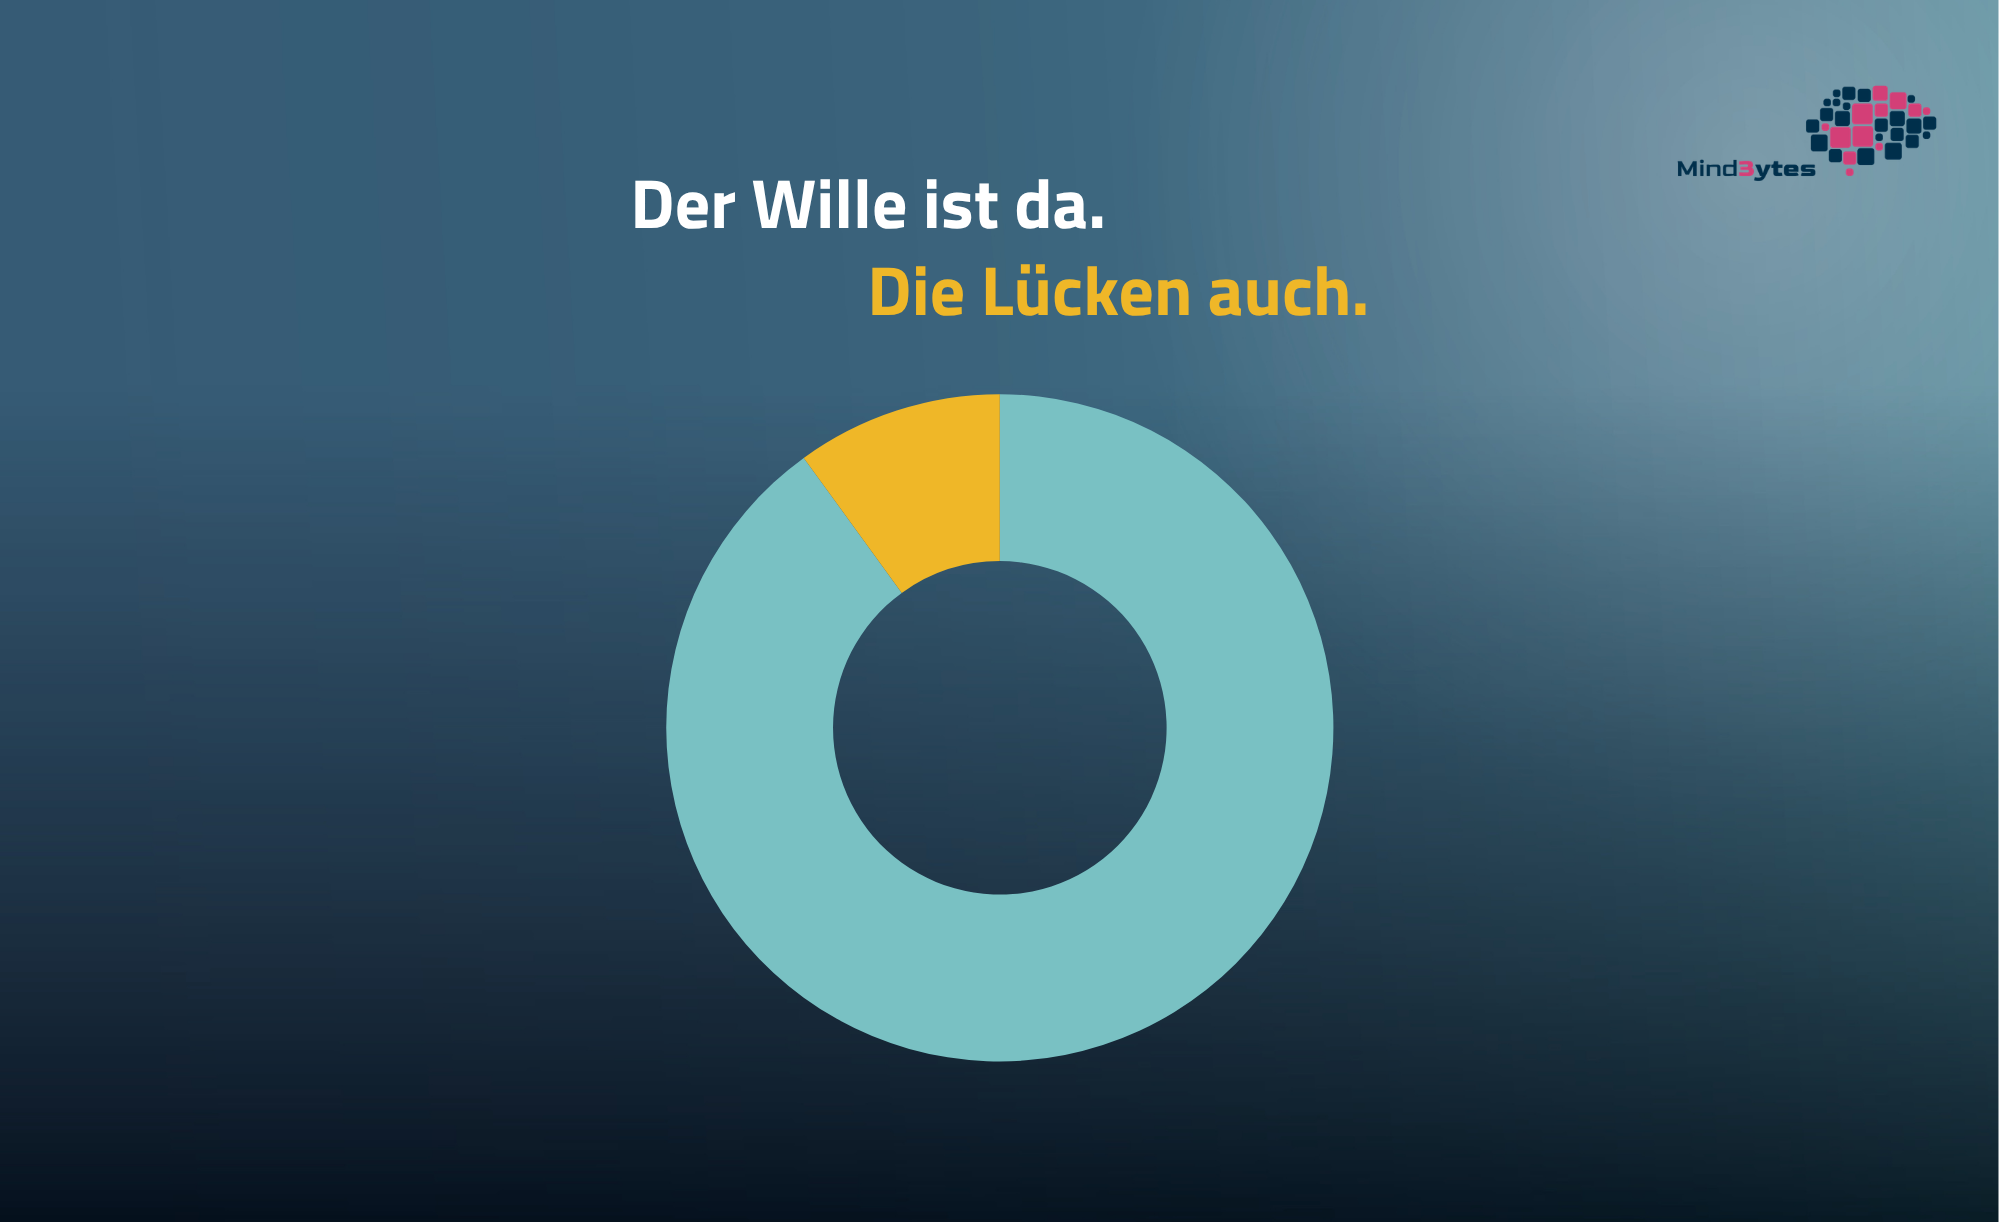
The intent is there. The gaps are, too.
That is how we describe what we see time and again in our projects: environments are improving. MFA rolled out, passkeys being introduced, Conditional Access, LAPS, AppLocker, a managed EDR.
And yet we still find vulnerabilities.
Not because the concepts are wrong, but because there is a gap between “introduced” and “complete” where we feel very much at home.
An attacker does not look for the rule. They look for its exception.
We see three patterns time and again:
1️⃣ Partial coverage – 90% rolled out, 10% stuck on legacy systems or a forgotten OU.
2️⃣ The exception is the attack vector – grown over time, never rolled back, rarely documented.
3️⃣ Detection without consequences – the alert exists. And then nothing happens.
In our guest post for Teal Technology Consulting, we show you 8 anonymous cases from real projects. Read the full blog post now.